

Step 1
Requirements Analysis
Our services deliver measurable results
We use AI across planning, design, and development to reduce waste, speed up delivery, and improve quality, without increasing budgets.
We joined at the very beginning, when Perpetuum Capital existed as a cybersecurity consultancy with deep ISO 27001 expertise but no digital product or online presence. We took full responsibility for product definition, UX design, website development, and the Sentinel SaaS from the first line of code through five years of continuous development.
Cybersecurity consultants and compliance experts who want to productize their ISO 27001 knowledge into a scalable SaaS platform. Also for organizations that need structured, tool-supported ISO 27001 certification and ongoing ISMS management without permanent consultant involvement.
 Product Design
 Wordpress
 214
Views
Karoly Aczel
Founder & CEO
The founding team had years of hands-on ISO 27001 consulting experience and knew exactly what companies needed to get certified - but everything was delivered manually, one client at a time. The gap was clear: companies wanting ISO 27001 certification were either paying expensive consultants for work that could be structured into a guided tool, or they were lost in documentation without any support. The idea was to build two things that work together: a professional website that builds trust and sells digital products, and a SaaS application called Sentinel that guides organizations through ISO 27001 certification and ongoing ISMS management without needing a consultant in the room.
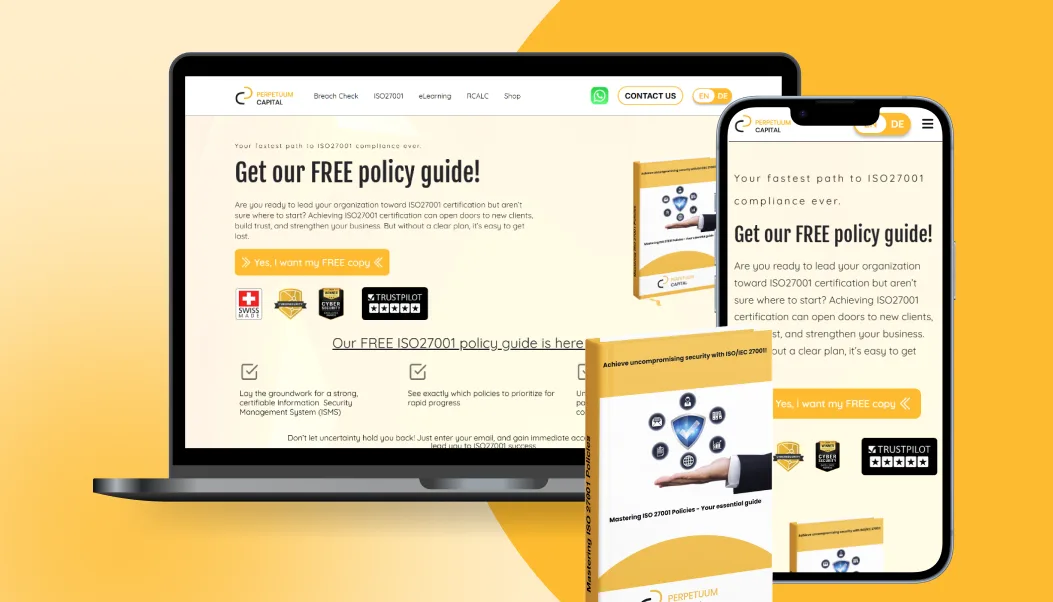
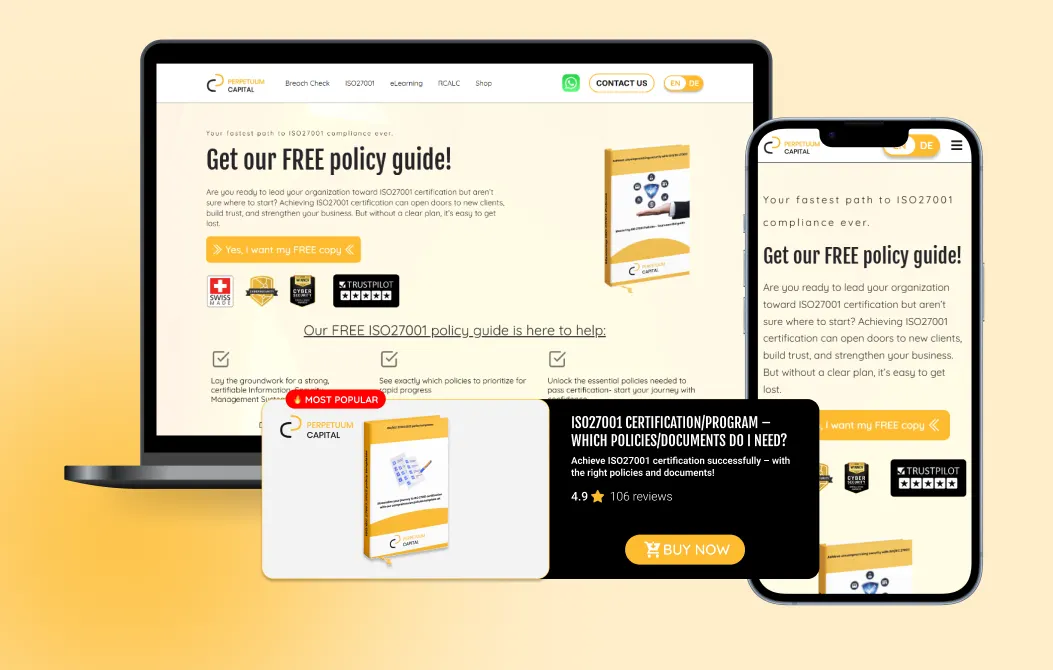
We designed and built PCapital as two connected products: a WordPress website with integrated WooCommerce shop, and Sentinel - a full-stack SaaS application for ISO 27001 management. The website handles discovery, trust-building, and sales - hosting content, landing pages, a breach checker tool, and a shop selling digital products from policy templates to the Sentinel subscription. Sentinel covers the full ISO 27001 lifecycle: gap analysis through structured chapter evaluations, guided implementation with maturity tracking per requirement, asset inventory management, document storage, and a unique Audit Mode that controls exactly what auditors see during (re-)certification. The admin panel gives the Perpetuum Capital team full control over clients, subscriptions, and platform content without engineering involvement. Together, the two products turned a one-person consultancy into a platform business that generates revenue around the clock and scales without adding headcount.
Step 1
Requirements Analysis
Step 2
Product & Design Concept
Step 3
Implementation
Step 4
Quality Assurance
Step 5
Deployment & Operation
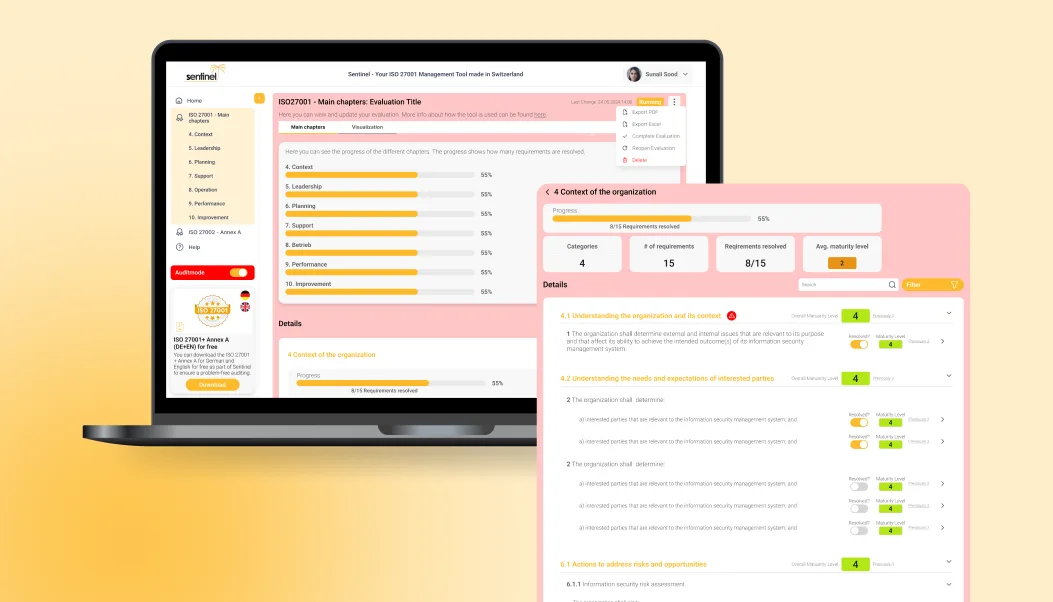
The heart of Sentinel is a structured evaluation engine that maps every section and requirement of ISO 27001 into a guided workflow. Organizations work through each requirement, assign a maturity level, assign responsible persons, add evidence, and link documents. Progress is tracked across all chapters in real time. Completed evaluations are locked and viewable but not editable, ensuring historical data integrity. This replaces spreadsheet-based gap analysis entirely and gives compliance teams a single, auditable source of truth.
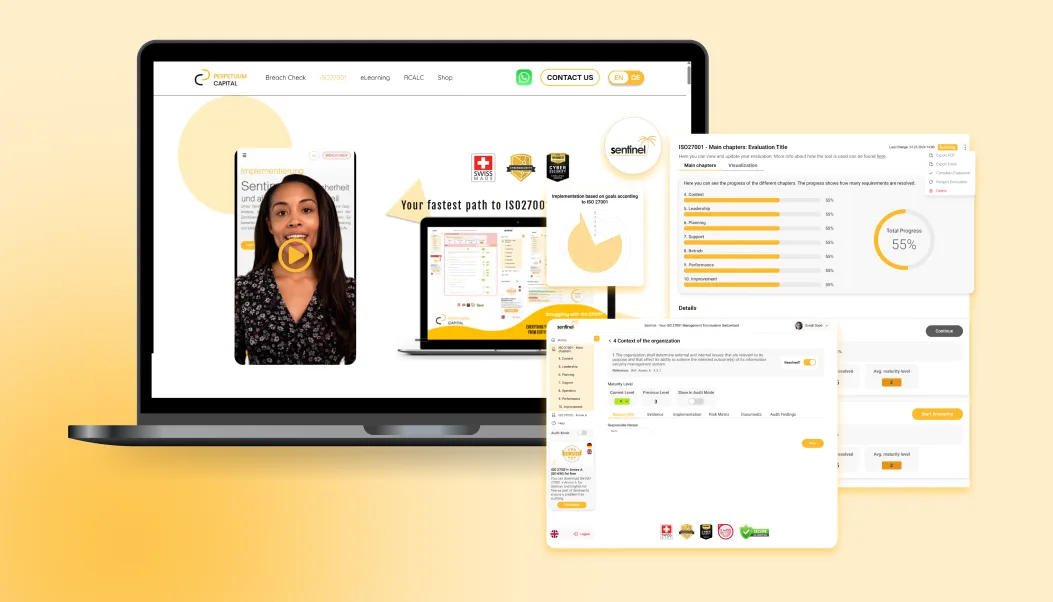
Sentinel's exclusive Audit Mode is the product's most differentiated feature - a separate view specifically designed for (re-)certification audit sessions. In Audit Mode, organizations can control exactly what auditors see: which chapters, which evidence, which notes. Sensitive internal remarks are hidden by default. The auditor-facing view is clean, structured, and presents only certified, verified data. Clients using Audit Mode report zero findings in their audits - the feature removes the most stressful part of certification entirely.
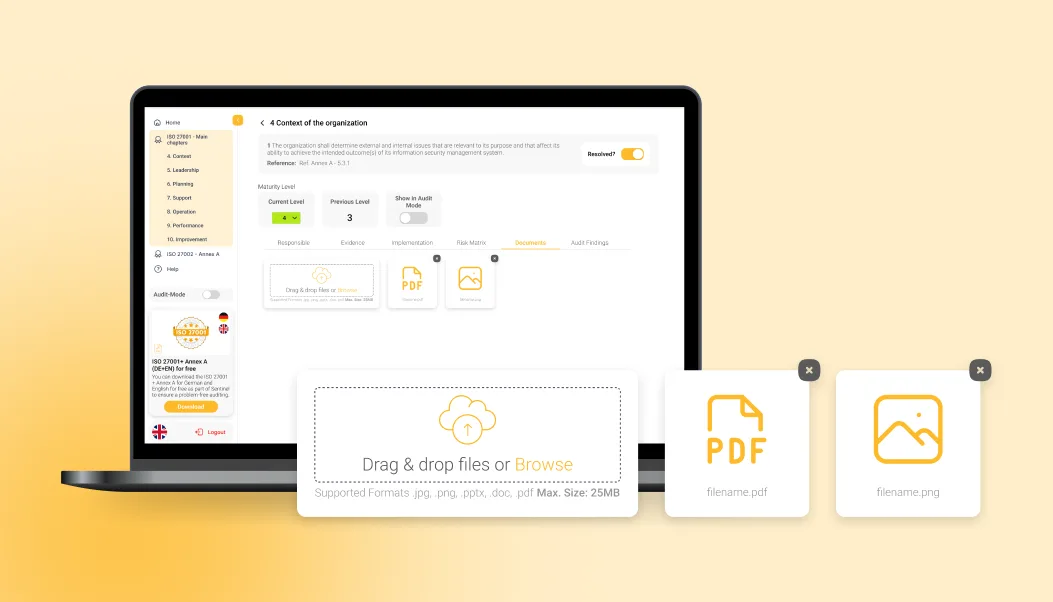
A full asset registry where organizations track all information assets required for ISO 27001 Annex A compliance. Each asset has a complete profile: type, owner, location, classification (Confidentiality, Integrity, Availability), asset value in EUR, lifecycle status, acquisition and disposal dates, and linked controls. Analytics views show total asset value by type and number of assets by location. The inventory replaces manual spreadsheets and directly links assets to the relevant ISO 27001 controls, making Annex A audits straightforward.
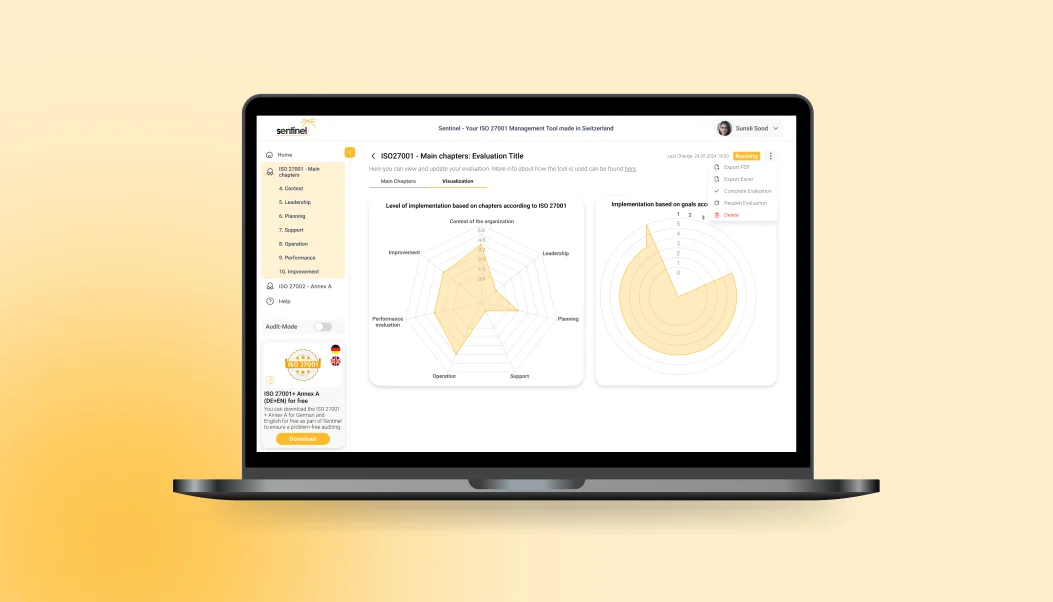
A radar chart and polar area chart give a real-time visual overview of ISO 27001 implementation readiness across all chapters. Charts update automatically as requirements are resolved. Organizations can see at a glance where they are strong and where gaps remain. Evaluations can be exported to Excel for management reporting or external consultant review. This turns a complex compliance process into a dashboard a non-expert can read and act on.
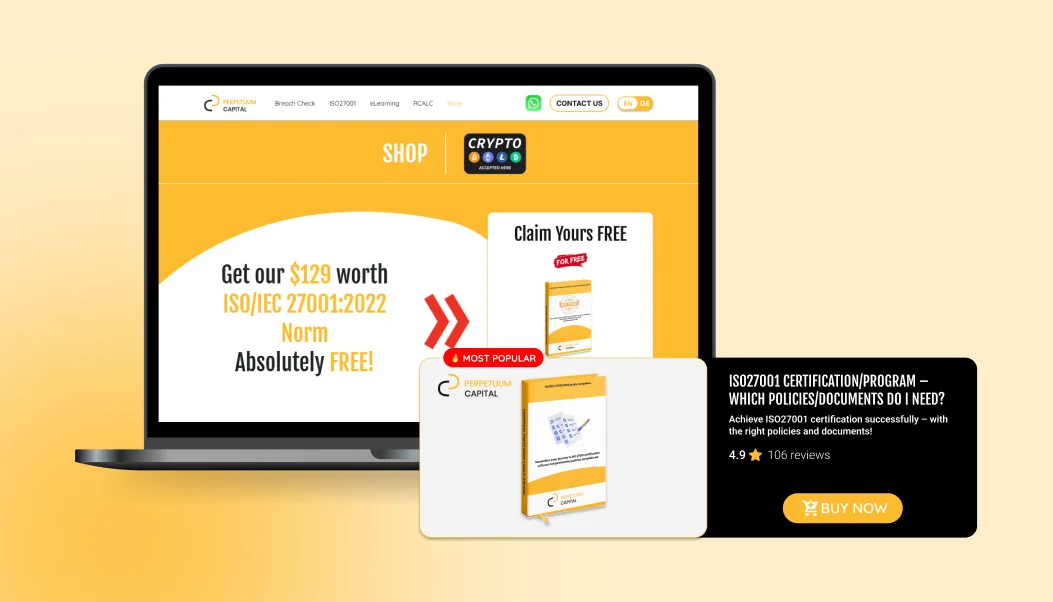
The WooCommerce-based shop sells a full range of ISO 27001 digital products: the Sentinel SaaS subscription, policy template sets, checklist tools, document review services, video training, SoA templates, and the asset inventory template. Products are available individually or as sets. Purchase triggers automated onboarding emails with next steps and Calendly booking links. The breach checker is available free with no signup required, driving top-of-funnel traffic. The shop enables Perpetuum Capital to generate revenue 24 hours a day from clients across the globe, independent of consulting capacity.
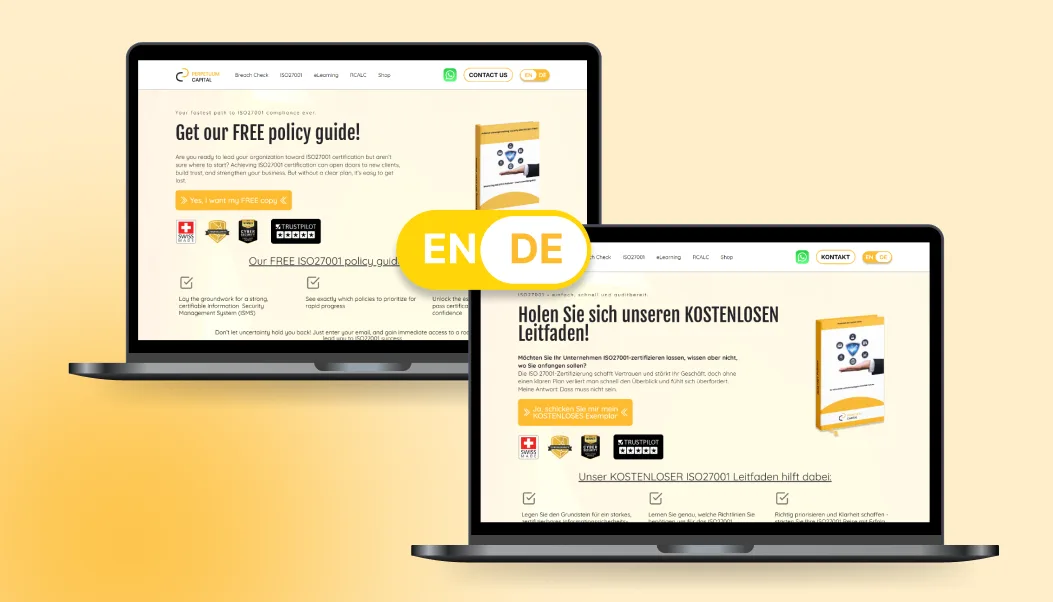
Both the website and the Sentinel application are fully bilingual in English and German. The ISO 27001 norm text, requirements, and guidance inside Sentinel are available in both languages. Users can switch language from within the app. The Annex A document is available for free download in both EN and DE directly from Sentinel. This opens the product to the full DACH market while supporting international clients, which is critical for a Swiss-based compliance tool.
The biggest challenge was translating a highly specialized compliance domain - ISO 27001 with its 93 Annex A controls, maturity models, and audit protocols - into a product that non-technical compliance professionals could use confidently without needing a consultant to explain it. The Audit Mode in particular required deep domain understanding. The feature had to control data visibility at a granular level without compromising the integrity of the underlying evaluation data. Getting the boundary between what auditors see and what the organization works with exactly right required multiple rounds of specification and testing with the founder as the domain expert. At the same time, the website and shop had to work as a trust-building and sales system in a market where buyers are skeptical - cybersecurity is a domain where credibility is everything.
Domain products require the domain expert as a permanent collaborator - not just a requirements source at the start. The ISO 27001 standard evolves, client feedback surfaces edge cases, and the competitive landscape shifts. Over five years, this has meant continuous refinement. Products built on deep domain logic need a long-term partner, not a one-time build.
Any expert who wants to productize their knowledge faces the same challenge: how do you take what is in your head and make it usable for someone who does not have your expertise? The answer is never a simple translation. It requires rethinking the domain logic as user flows, validating every assumption with real users, and being willing to iterate for years.
If you want to turn your expertise into a product, start with the workflow your clients struggle with most - not with the features you want to build. The domain logic is the product. Everything else is just the interface around it.
The most special part of building Sentinel was designing and implementing the Audit Mode. On the surface it sounds like a simple filter - show auditors only what they need to see. In practice it required us to think from the perspective of an ISO 27001 auditor, understand exactly what triggers a finding, and build a data layer that could present the same underlying information in two completely different contexts without contaminating either. We spent weeks in deep sessions with the founding team walking through real audit scenarios. What does an auditor open first? What would cause an immediate red flag? What should never be visible? Every answer changed something in the data model, the UI, or the access logic. It was the kind of work that looks invisible in the final product - because when it works, auditors see exactly what builds confidence and nothing that creates doubt. The first time a client went through a real certification audit using Audit Mode and came back with zero findings - that was the moment we knew the feature had done exactly what it was designed to do. That outcome is not visible in any screenshot of the product. It lives in the audit report of a company that is now ISO 27001 certified because the tool gave them the right structure at the right moment.
 Karoly Aczel
Founder & CEO
5.0
I came to Vitec with deep ISO 27001 knowledge but no product. They built the website, the SaaS, and the shop from scratch. Everything works together - the content, the design, the tool. Clients now find us, trust us, and buy - without a sales call.
Every successful project leaves behind measurable results and a clear path forward.
The references below show how we work, what we deliver, and the outcomes our partners achieve with us.
 STRATEGY
 UI/UX
 MARKETPLACE
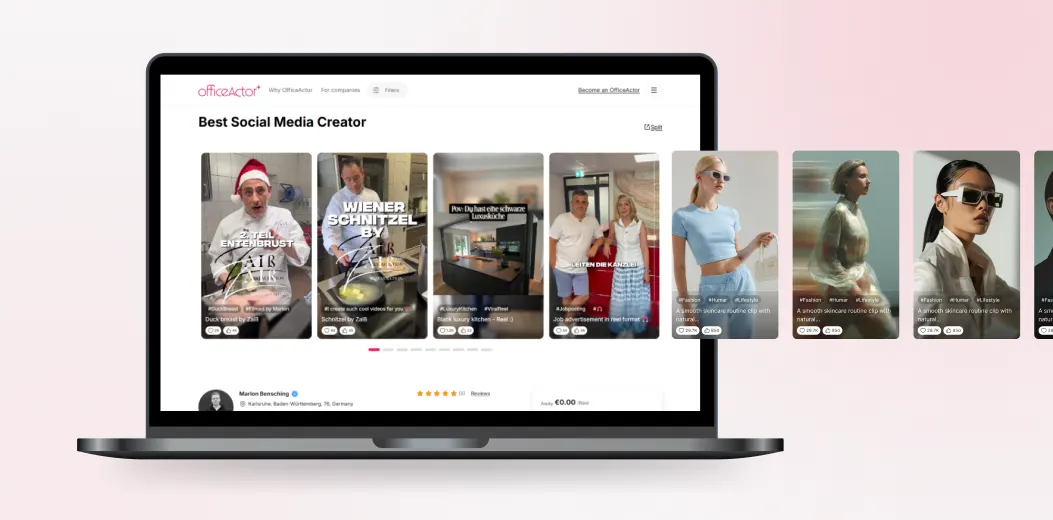
OfficeActor - End-to-End Influencer Booking Platform
Marlon B.
Founder & CEO, OfficeActor
Marlon B. saw a clear gap in the market: companies wanting to collaborate with influencers had no structured way to find, evaluate, and book them. Everything happened through DMs, spreadsheets, and informal agreements. At the same time, influencers had no professional tool to manage incoming requests, track contracts, or get paid reliably. The idea was to build a two-sided platform that gives both parties a clean, structured workflow - from discovery to signed contract to payment.
0 manual booking steps
Use case
 STRATEGY
UI/UX
 MOBILE APP
 BACK-END
 ADMIN
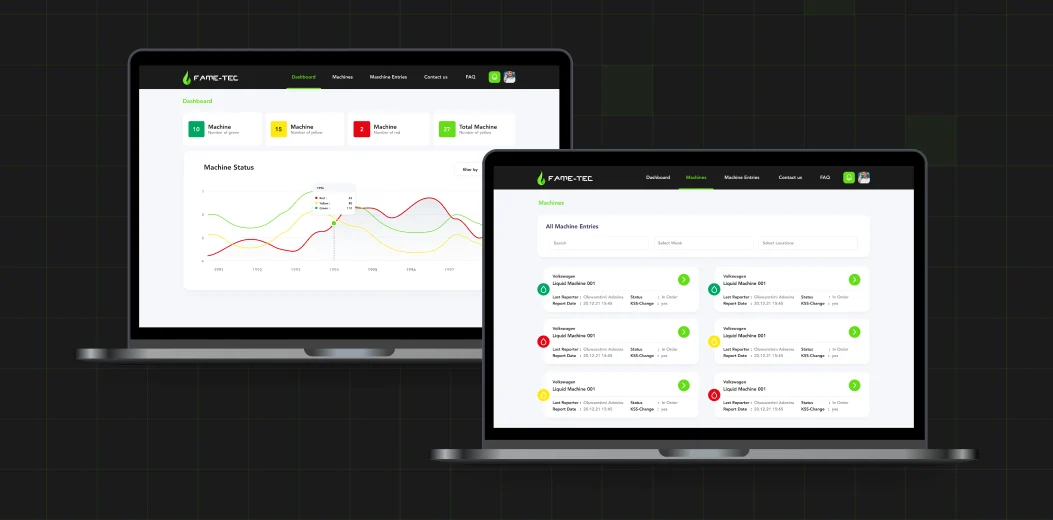
fame-tec - Digitalizing Industrial Fluid Monitoring
Yunus-Emre Akarca
CEO, fame-tec GmbH
fame-tec is a fluid management company responsible for maintaining liquid conditions in on site industrial machines.Manual processes made it difficult to track machine status, detect issues early, and document maintenance reliably.The idea was to replace paper based workflows with an automated digital solution that allows employees to access machine data instantly, update fluid values on site, and give customers transparency into the condition of their machines.Reducing manual effort, preventing errors, and improving operational control were the core motivations behind the project.
35%
fewer support requests
Use case


 Behance


